Register for part 2 of our Device Identity Webinar Series!

Hardware-backed device identity for Fleet

Fleet delivers real-time visibility and orchestration across diverse device fleets. Smallstep adds hardware-backed device identity to enforce trust for developer workflows, AI-enabled tools, and MCP-based automation.

Book a demo
background gradientbackground texture
Devices iconEasy device revocation
Automate config & renewal iconAutomated cert lifecycle
Certificate iconEliminate credential theft
MDM integration iconEnhanced Visibility & Compliance
Cross-platform coverageCross-OS Device Attestation
Network iconOpen & Extensible Architecture

Even the best MDMs alone aren't enough

When Smallstep is added to Fleet, a device's hardware identity becomes an authentication factor. Instead of relying solely on shared secrets and user credentials, Smallstep silently verifies device trust —blocking unauthorized machines without adding friction for users.

Together Smallstep and Fleet can:

  • Support hardware device attestation
  • Support ACME device attestation
  • Support conditional access
  • Support device inventory
  • Check if a device is real or a cloned VM

Fleet seamlessly integrates with Smallstep

Zero-touch device configuration

Smallstep automatically pushes secure configuration profiles and credentials for Wi-Fi, VPN, and SaaS apps to all verified devices. Your IT team enjoys streamlined, error-free enrollments, freeing them from tedious manual processes while ensuring robust, reliable security across your entire device fleet.
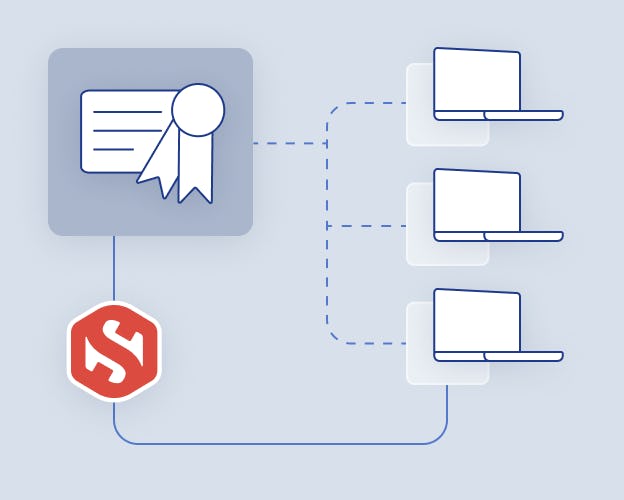
Easy certificate lifecycle maintenance

Hands-free certificate management

Say goodbye to manual certificate renewals and revocation headaches. Smallstep proactively monitors certificate lifecycles—automatically renewing credentials before expiration and immediately revoking access for offboarded or compromised devices. Reduce administrative overhead, eliminate manual errors, and keep device security always up-to-date.

Fleet + Smallstep data sheet

Get the data sheet

When Smallstep is added to Fleet, a device's hardware identity becomes an authentication factor. Instead of relying solely on shared secrets and user credentials, Smallstep silently verifies device trust, blocking unauthorized machines without adding friction for users.

Download
background gradient

Strengthen your Fleet inventory

Passwords and posture checks alone can’t guarantee that devices in your Fleet device inventory are trusted. Hardware-backed keys and attestation dramatically raise the bar against attackers. Learn how hardware-backed device identity can add cryptographic device proof to your MDM posture.

Book a demo

FAQs Smallstep + Fleet

The Smallstep + FleetDM integration combines FleetDM’s open-source MDM and device inventory with Smallstep’s device identity and certificate automation.

Together, they turn managed endpoints into cryptographically verified devices that can securely access Wi-Fi, VPNs, SaaS apps, and internal services.

FleetDM tells you what devices you manage. Smallstep ensures those devices can prove who they are cryptographically.

This closes the gap between device management and device trust, eliminating reliance on passwords, shared secrets, or user-only authentication.

FleetDM provides authoritative device inventory and management signals. Smallstep consumes that inventory to issue hardware-bound certificates only to approved devices.

If a device is removed from FleetDM, its certificates can be automatically revoked.

The integration supports macOS, Windows, and Linux devices managed by FleetDM.

Smallstep leverages platform security hardware (TPMs and Secure Enclaves) where available to provide high-assurance device identity.

Smallstep issues short-lived, automatically rotated certificates for device authentication.

These certificates can be used for Wi-Fi (802.1X), VPNs, Zero Trust access, SaaS apps, SSH, and internal web services.

SCEP relies on shared secrets and offers no cryptographic proof of device identity.

With Smallstep, certificates are issued using modern enrollment methods and device attestation, making credentials non-exportable and resistant to phishing or replay attacks.

No. FleetDM remains your MDM and device inventory. Smallstep provides device identity and certificate lifecycle management.

They are complementary tools that together deliver secure, zero-trust device access.

Yes. FleetDM ensures the device is managed, and Smallstep ensures the device can cryptographically authenticate.

This allows you to enforce Zero Trust policies based on both device posture and device identity.

When a device is removed from FleetDM, Smallstep can automatically revoke its certificates.

This immediately cuts off access to protected resources without relying on user offboarding or manual cleanup.

This integration is ideal for security, IT, and platform teams that want stronger guarantees than traditional MDM or MFA alone.

If you already use FleetDM and want hardware-backed device trust without deploying another MDM, this integration is designed for you.